The practical guide for business owners · $12.99

7 Cybersecurity Questions

Every business owner should ask their IT provider. The right questions today can prevent a crisis tomorrow. Purchase for $12.99 and receive free access to our online community, launching October 15.

Cover of 7 Cybersecurity Questions Every Business Owner Should Ask Their IT Provider

By Thomas M. McClendon

Discover  ·  Defend  ·  Strengthen  ·  Adapt

The illusion of expertise

Everything seems fine. Until you ask one simple question.

Invoices are being sent. Customers are being served. Computers are humming. But calm is not the same as confidence, and “we have backups” is not the same as a tested recovery plan.

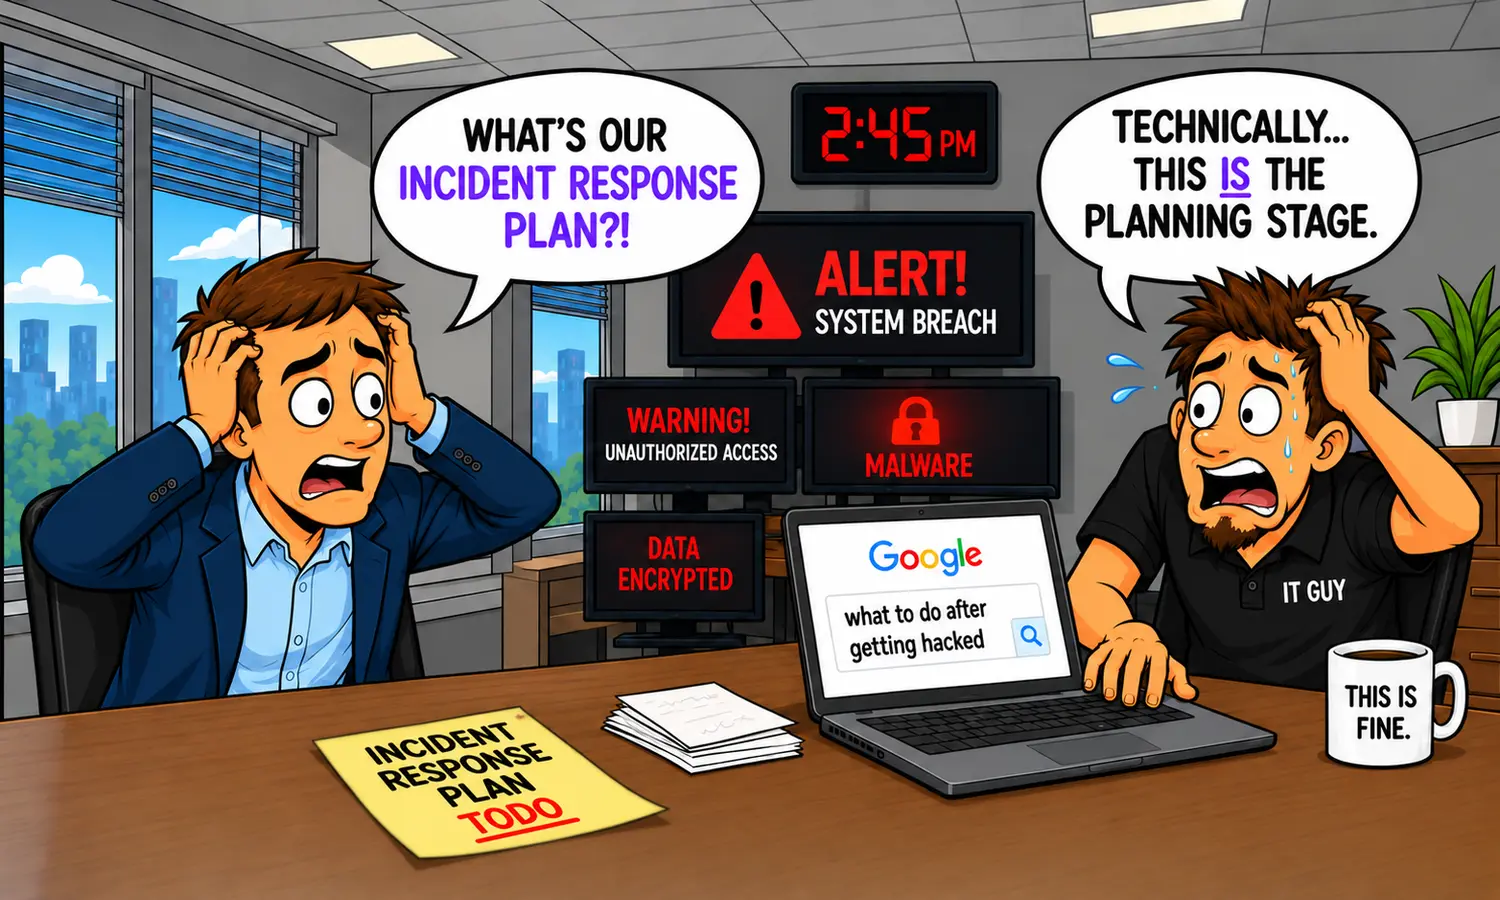
Cinematic panel 1 showing a business owner asking his IT provider about backup readiness
Panel 1 of 4
Cinematic panel 2 showing a business owner asking his IT provider about backup readiness
Panel 2 of 4
Cinematic panel 3 showing a business owner asking his IT provider about backup readiness
Panel 3 of 4
Cinematic panel 4 showing a business owner asking his IT provider about backup readiness
Panel 4 of 4

Clarity is a business control

Ask. Listen. Verify.

You do not need to be a cybersecurity expert. You need clear answers, evidence, and the confidence to keep asking when something does not make sense.

Illustration for question 1: How do we know our backups actually work?

Question 1

How do we know our backups actually work?

A backup is only useful if it can be restored. Ask how often restores are tested, who reviews the results, and whether a clean copy is protected away from the systems it backs up.

Listen for A recent test date, documented results, recovery targets, and a clear owner.
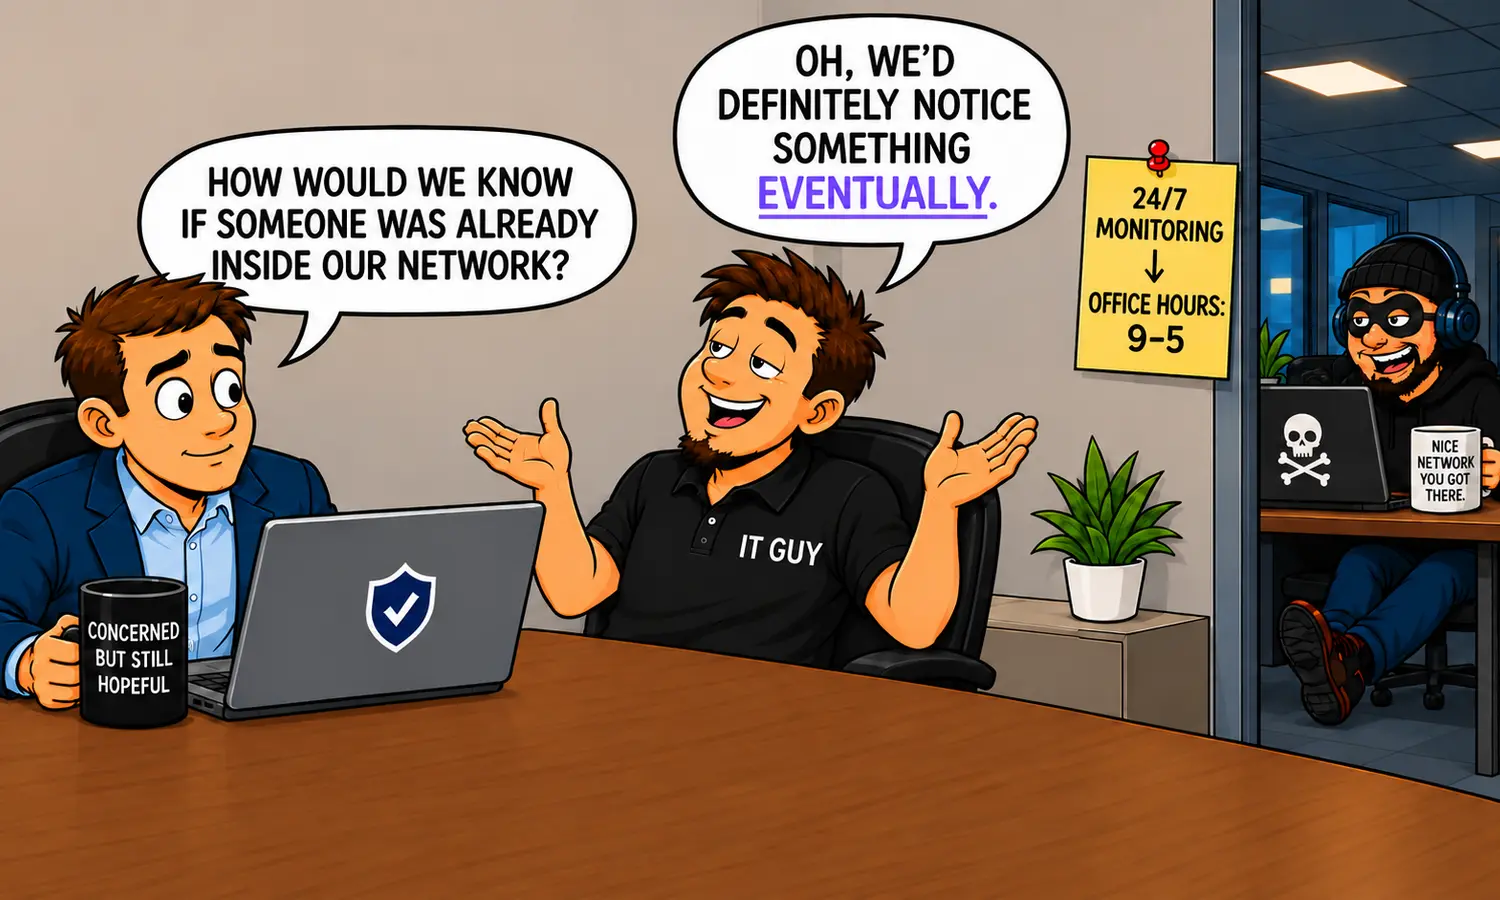
Illustration for question 2: How would we know if someone was already inside our network?

Question 2

How would we know if someone was already inside our network?

Prevention matters, but detection determines how quickly suspicious activity becomes a contained event instead of a prolonged business crisis.

Listen for Continuous monitoring, meaningful alerts, named responders, and after-hours coverage.
Illustration for question 3: What is our incident response plan?

Question 3

What is our incident response plan?

When pressure is high, people should not be inventing the plan. Roles, communication paths, evidence handling, and recovery priorities should already be understood.

Listen for A written plan, assigned roles, current contacts, and proof that the plan has been exercised.
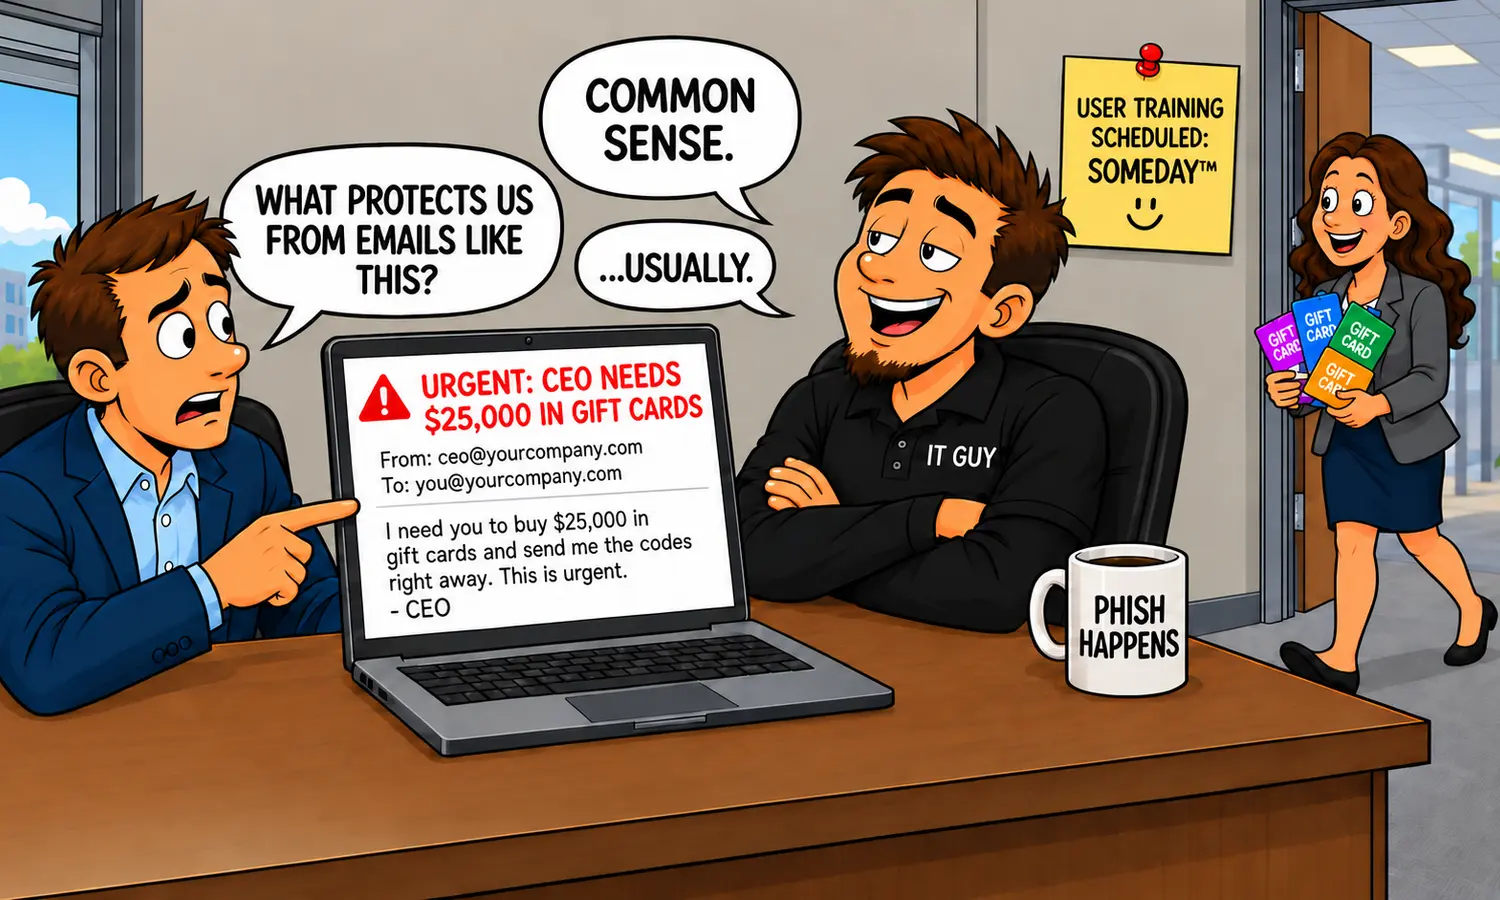
Illustration for question 4: What protects us from email scams and impersonation?

Question 4

What protects us from email scams and impersonation?

Email is where technical controls and human judgment meet. Protection should cover malicious messages, account takeover, domain impersonation, and payment fraud.

Listen for Layered filtering, MFA, SPF/DKIM/DMARC, training, and a simple reporting process.
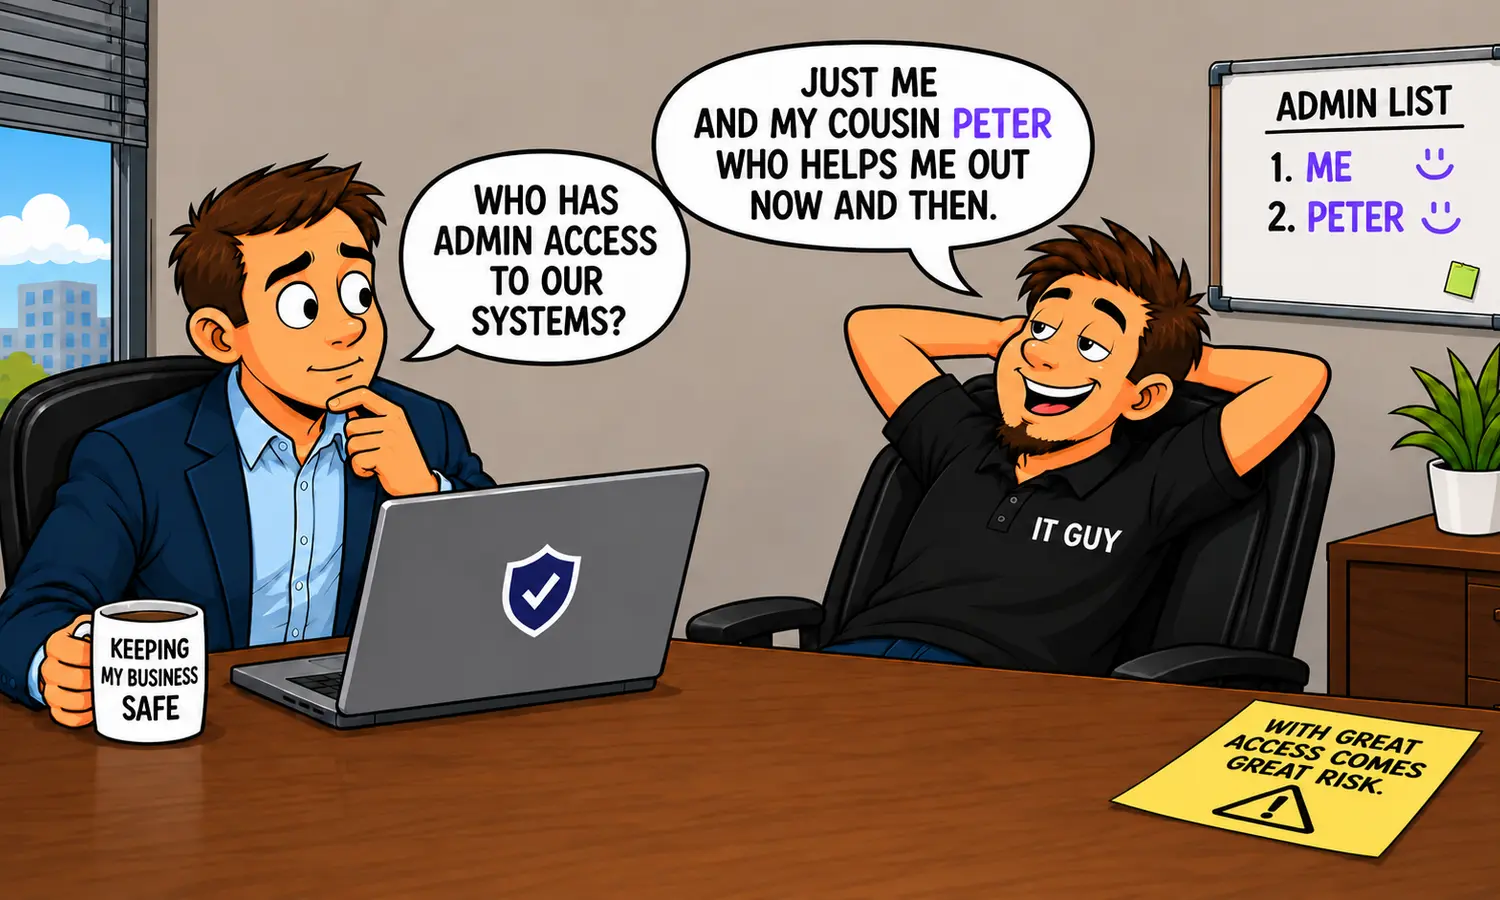
Illustration for question 5: Who has administrative access to our systems?

Question 5

Who has administrative access to our systems?

Powerful access should be rare, deliberate, and reviewable. Shared accounts and forgotten privileges create risk that is difficult to see until something goes wrong.

Listen for A current access list, individual accounts, MFA, approval controls, and regular review.
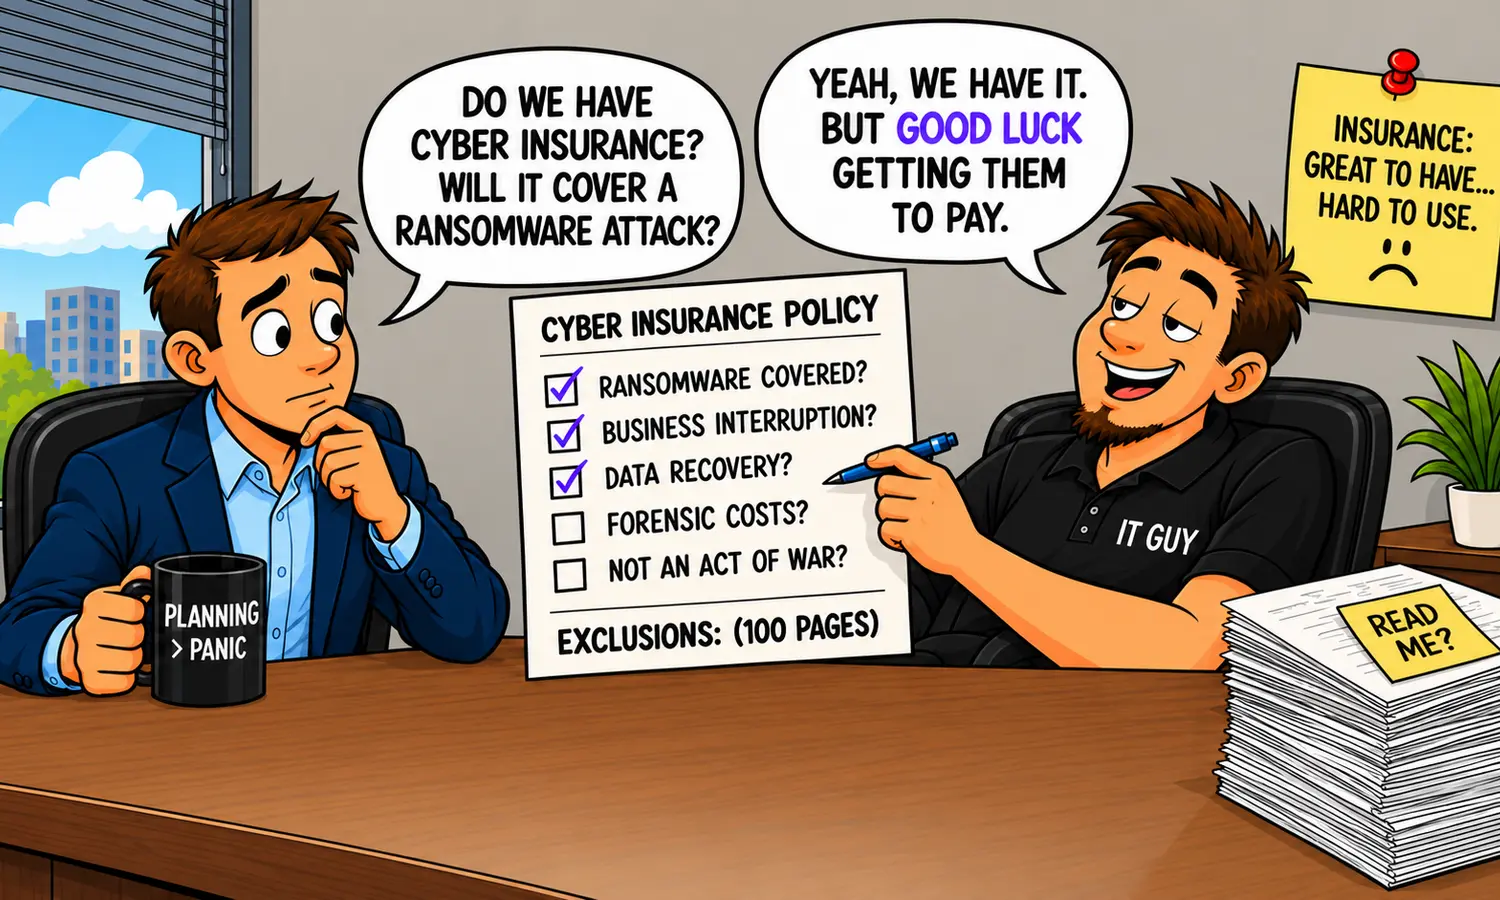
Illustration for question 6: Does our cyber insurance actually match our risk?

Question 6

Does our cyber insurance actually match our risk?

A policy is not a substitute for security, and assumptions can become expensive exclusions. Your controls, application answers, coverage, and response plan should agree.

Listen for Clear coverage limits, known exclusions, control requirements, and incident notification steps.
Illustration for question 7: What are our rules for AI and data protection?

Question 7

What are our rules for AI and data protection?

AI can create real value, but unapproved tools can expose confidential information. People need practical boundaries that keep innovation useful and accountable.

Listen for An approved-tool list, data rules, human review, training, and a process for exceptions.

One important rule

If you do not understand the answer, keep asking questions.

If the answer is not a clear, evidence-backed “yes,” treat it as a “no” until it can be verified.

Thomas M. McClendon, founder and president of Citadel Networks

About the author

Thomas M. McClendon

Thomas is the founder and president of Citadel Networks, a cybersecurity, compliance, and managed IT services company serving small and midsize businesses. Known as the Friendly Cyber Avenger, he turns cyber risk into practical action without unnecessary complexity or fear.

A Marine Corps veteran with more than 25 years in technology and cybersecurity, Thomas believes cybersecurity is a business responsibility, not simply an IT problem.

The book + a website-exclusive bonus

Own the guide. Join the conversation.

Purchase the complete 82-page book for $12.99 and bring it to your next technology meeting. Your website purchase also includes free access to our online community when it launches October 15.